WEB AS ONGOING THREAT VECTOR: CASE STUDIES FROM EUROPE AND ASIA PACIFIC
No ratings
Presented at First 2017 by
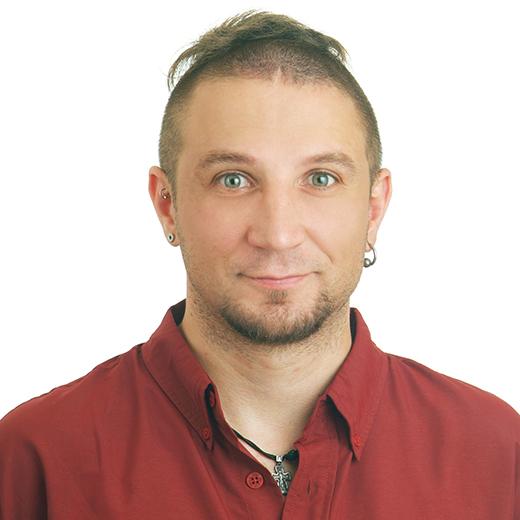

Fyodor is a researcher with TrendMicro Taiwan as well as a Ph.D. candidate at EE, National Taiwan University. An early Snort developer, and open source evangelist as well as a "happy" programmer. Prior to that, Fyodor professional experience includes several years as a threat analyst at Armorize and over eight years asa information security analyst responding to network, security breaches and conducting remote network security assessments and network intrusion tests for the majority of regional banking, finance, semiconductor and telecommunication organisations. Fyodor is an active member of local security community and has spoken at a number of conferences regionally and globally. Vladimir recently joined Trend Micro FTR team. Active for over 15 years in information security projects and research, he previously built and led incident response teams at some of Fortune 500 companies, was head of Incident Response Team at Positive Technologies since 2014, and holds a university degree in applied mathematics and information security. He participates in various projects for leading financial, industrial, and telecom companies. His main interests lie in network traffic analysis, incident response, botnet and cybercrime investigations. Vladimir regularly appears at high-profile international conferences such as FIRST, CARO, HITB, Hack.lu, PHDays, ZeroNights, POC, Hitcon, and many others. This presentation covers several case studies from incident response sessions in Europe and Asia Pacific region. We analyse attackers tools, exploitation chain, and artefacts discovered on compromised assets in each particular case. We do a comparative case study of several attack attack vectors that leverage web browser components to identify signs of compromise that should be examined by forensic teams to trace such attacks to 'patient-zero' cause of breach. We demonstrate several cases where attackers used multi-staged exploitation chains and perform fingerprinting of target systems identifying systems suitable for further compromise before serving additional malicious payload.